
Setting Up ADAudit Plus Vulnerability Debugging Environment
0x00 Preface
This article records the details of setting up an ADAudit Plus vulnerability debugging environment from scratch and introduces methods to obtain database user passwords.
0x01 Introduction
This article will cover the following content:
ADAudit Plus Installation
ADAudit Plus Vulnerability Debugging Environment Configuration
Database User Password Acquisition
0x02 ADAudit Plus Installation
1. Download
Full version download address: https://archives2.manageengine.com/active-directory-audit/
2. Installation
Installation reference: https://www.manageengine.com/products/active-directory-audit/quick-start-guide-overview.html
3. Test
Access https://localhost:8081
0x03 ADAudit Plus Vulnerability Debugging Environment Configuration
The method is basically similar to the vulnerability debugging environment configuration of Password Manager Pro
1. Enable debugging function
(1) Locate the configuration file
Check the information of Java processes; there are two Java processes here, corresponding to two different parent processes wrapper.exe, as shown in the figure below
The process parameters of wrapper.exe are as follows:
"C:\Program Files\ManageEngine\ADAudit Plus\bin\Wrapper.exe" -c "C:\Program Files\ManageEngine\ADAudit Plus\bin\..\conf\wrapper.conf"
"C:\Program Files\ManageEngine\ADAudit Plus\bin\wrapper.exe" -s "C:\Program Files\ManageEngine\ADAudit Plus\apps\dataengine-xnode\conf\wrapper.conf"
The configuration file to modify here is C:\Program Files\ManageEngine\ADAudit Plus\conf\wrapper.conf
(2) Modify the configuration file to add debugging parameters
Find the position to enable the debugging function:
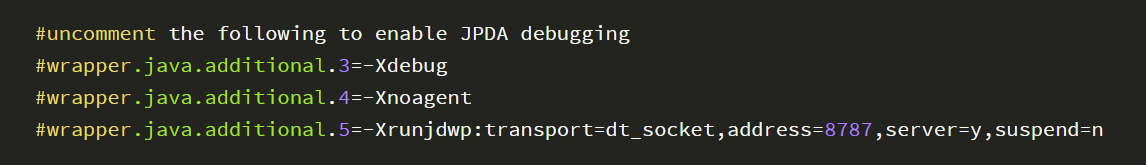
Change it to:
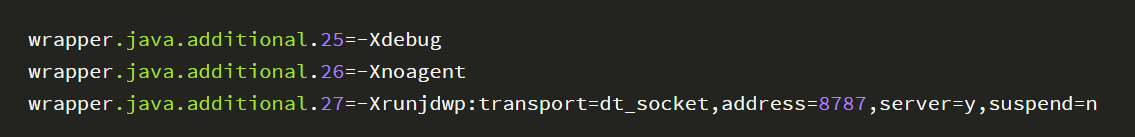
Note:
The sequence numbers need to be incremented one by one; here, change wrapper.java.additional.3=-Xdebug to wrapper.java.additional.25=-Xdebug
(3) Restart related processes
Close the process wrapper.exe and its corresponding child process java.exe
Execute the command in the command line:

2. Location of common jar packages
Path: C:\Program Files\ManageEngine\ADAudit Plus\lib
The implementation files for web functions are AdventNetADAPServer.jar and AdventNetADAPClient.jar
3. IDEA Settings
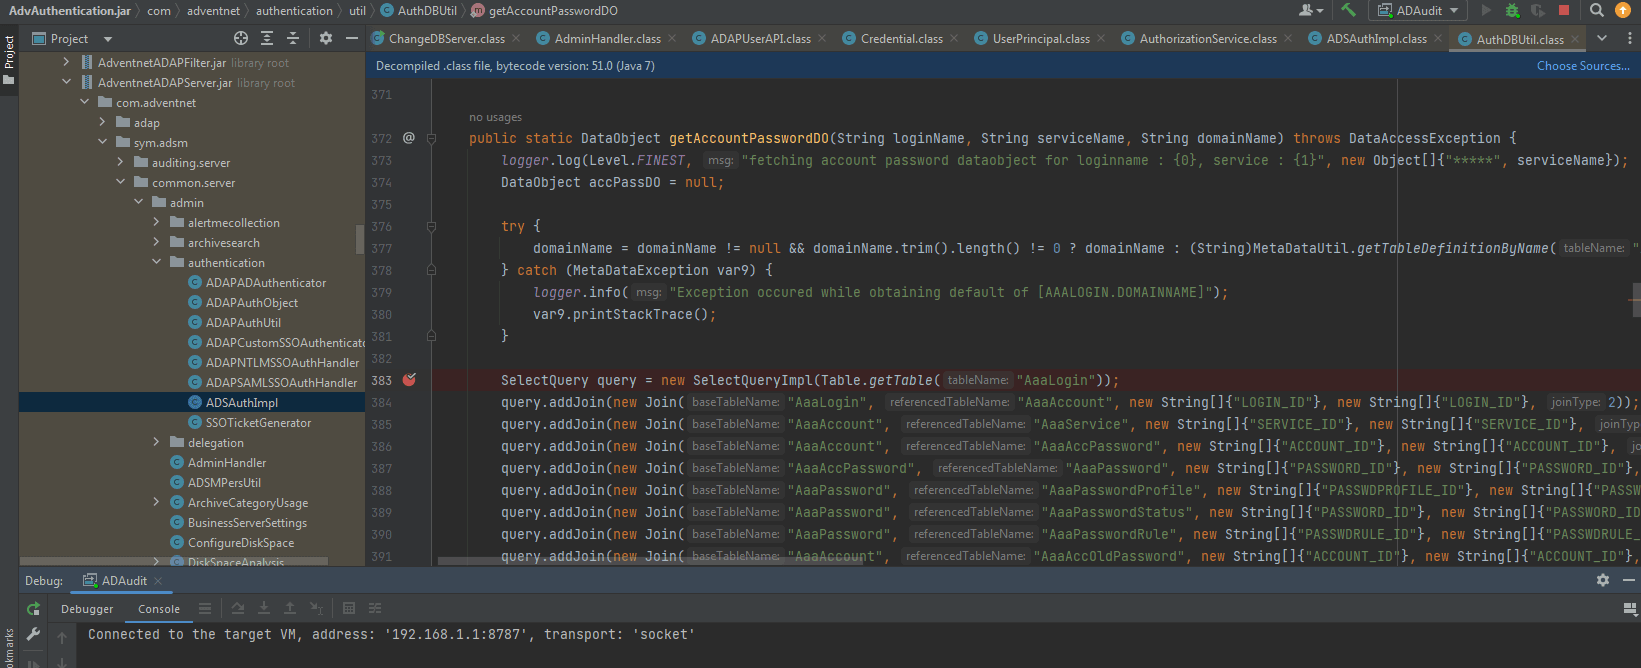
Set to Remote JVM Debug; the successful remote debugging is shown in the following figure
0x04 Obtaining Database User Passwords
Under default configuration, ADAudit Plus uses PostgreSQL to store data, and two login users are configured by default: adap and postgres
1. Obtaining the password for user adap
Configuration file path: C:\Program Files\ManageEngine\ADAudit Plus\conf\database_params.conf, content example:
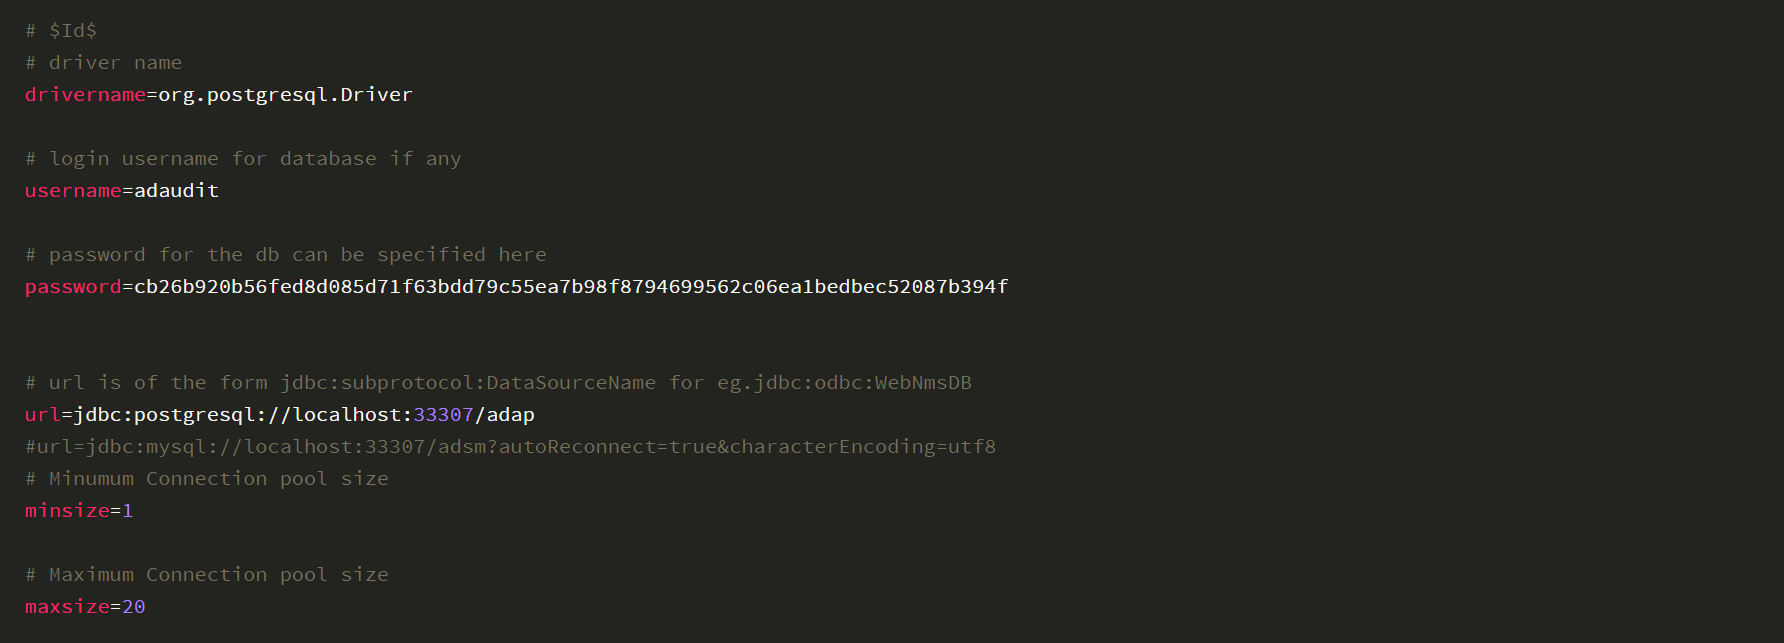
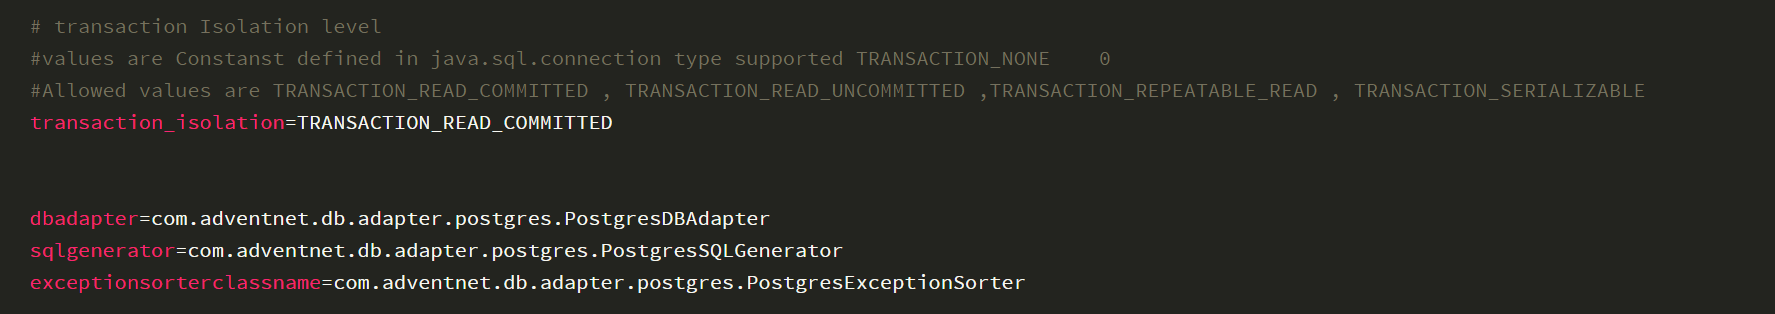
Among them, the password is encrypted; the encryption and decryption algorithm is located in: com.zoho.framework.utils.crypto->CryptoUtil.class within C:\Program Files\ManageEngine\ADAudit Plus\lib\framework-tools.jar
After code analysis, the following decryption method is obtained:
The key is stored in a fixed location at C:\Program Files\ManageEngine\ADAudit Plus\conf\customer-config.xml, content example:
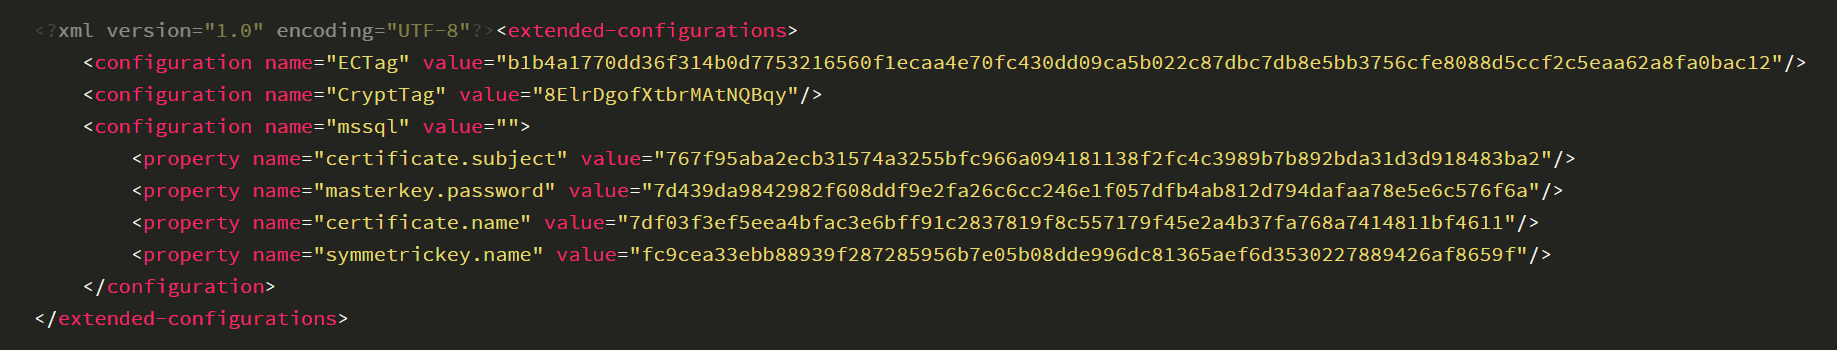
Get the key: CryptTag is 8ElrDgofXtbrMAtNQBqy
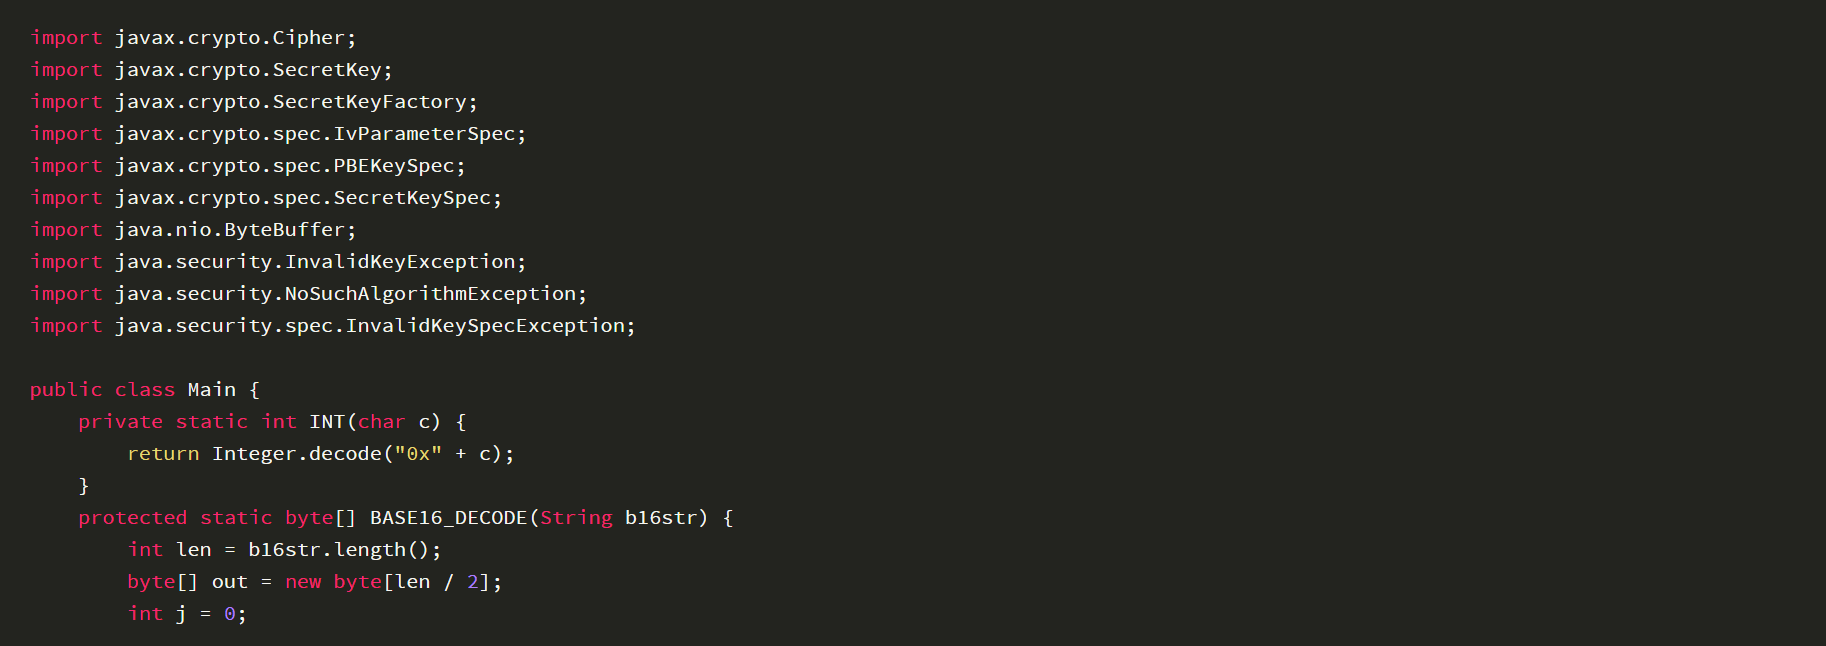
Based on the above-obtained ciphertext cb26b920b56fed8d085d71f63bdd79c55ea7b98f8794699562c06ea1bedbec52087b394f and key 8ElrDgofXtbrMAtNQBqy, write a decryption program. The code is as follows:
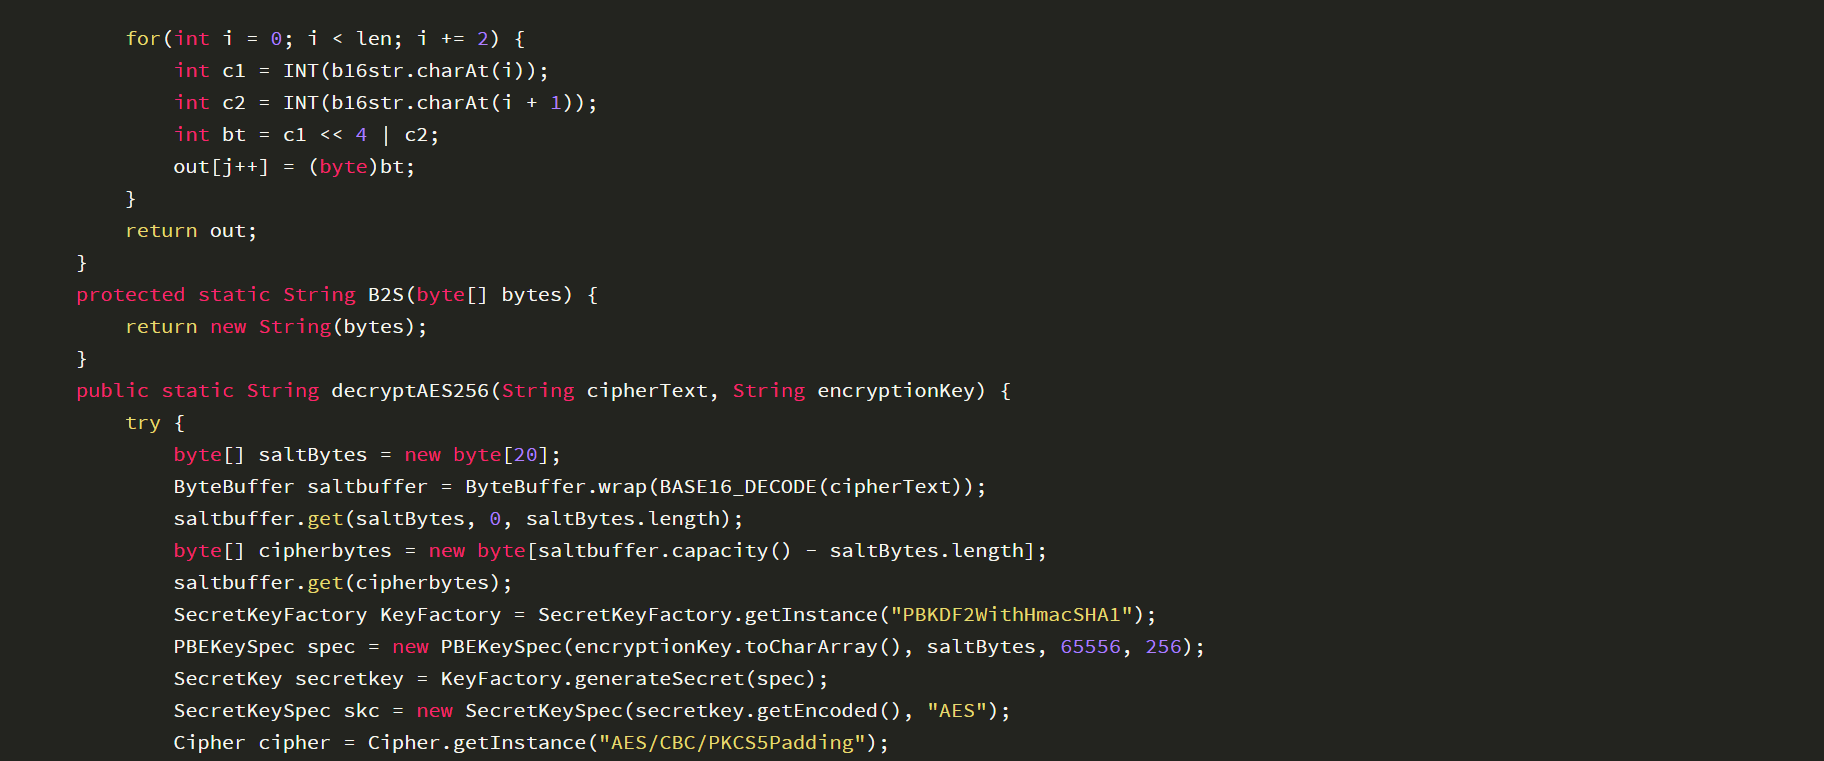
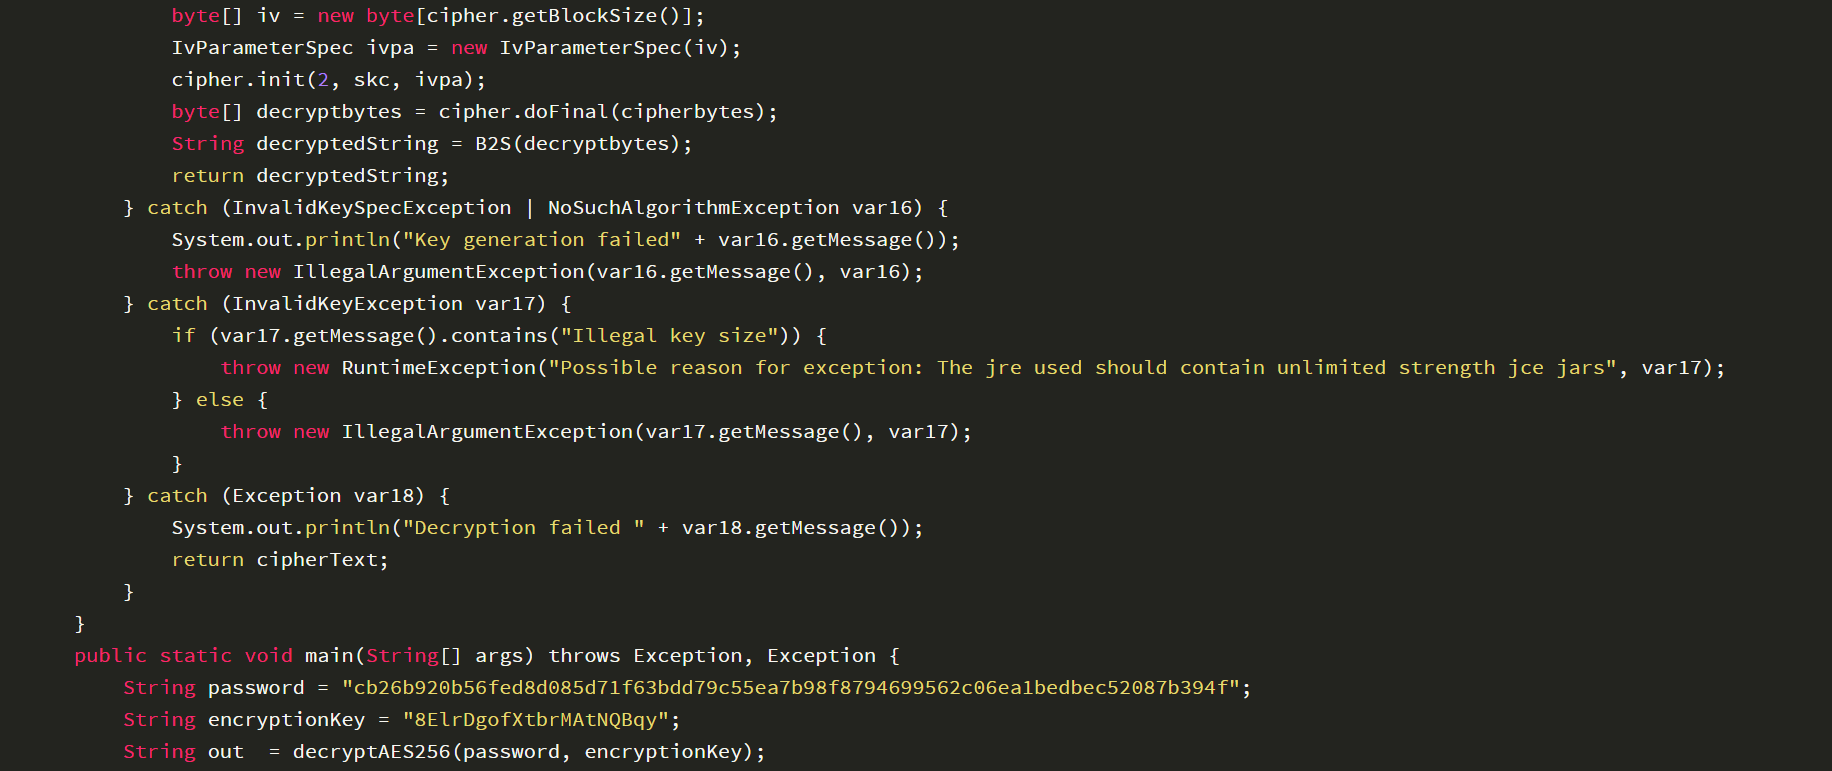

After running the program, the decryption result is obtained: Adaudit@123$
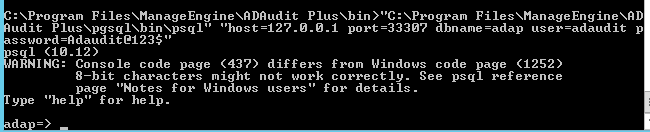
Splice the database connection command: \"C:\\Program Files\\ManageEngine\\ADAudit Plus\\pgsql\\bin\\psql\" \"host=127.0.0.1 port=33307 dbname=adap user=adaudit password=Adaudit@123$\"
Connection successful, as shown in the following figure
2. Obtaining the password for user postgres
The password is hard-coded in com.adventnet.sym.adsm.common.server.mssql.tools->ChangeDBServer.class->isDBServerRunning() within C:\\Program Files\\ManageEngine\\ADAudit Plus\\lib\\AdventnetADAPServer.jar, as shown in the following figure
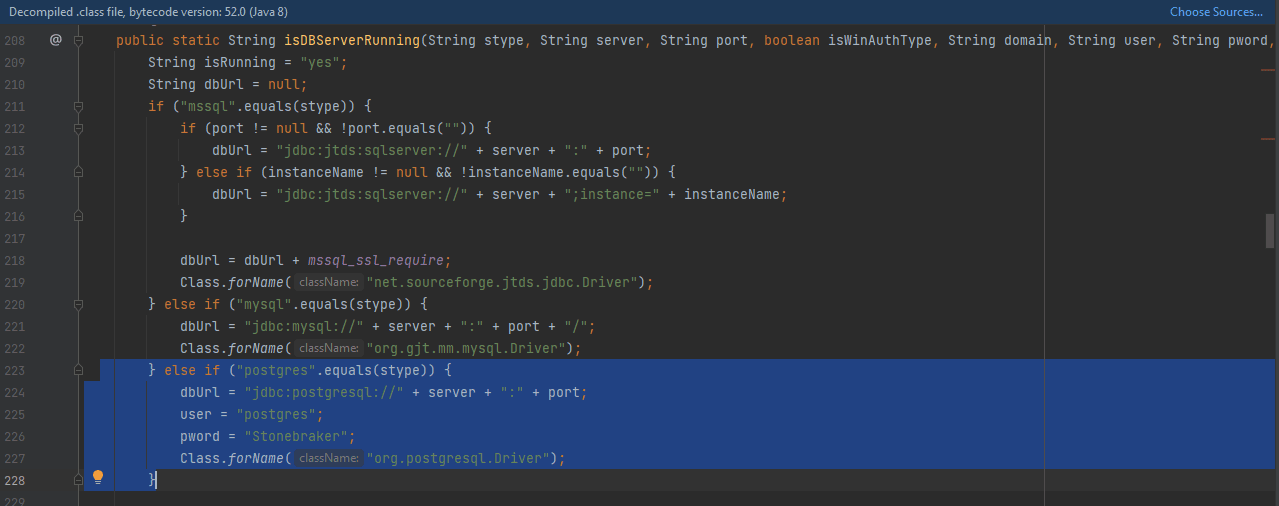
The password for user postgres is obtained as Stonebraker
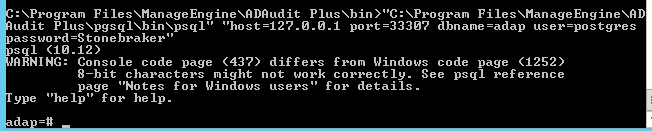
Splice the database connection command: \"C:\\Program Files\\ManageEngine\\ADAudit Plus\\pgsql\\bin\\psql\" \"host=127.0.0.1 port=33307 dbname=adap user=postgres password=Stonebraker\"
Connection successful, as shown in the following figure
An example command to connect to the database and perform database operations in one line: \"C:\\Program Files\\ManageEngine\\ADAudit Plus\\pgsql\\bin\\psql\" --command=\"SELECT * FROM public.aaapassword ORDER BY password_id ASC;\" postgresql://postgres:[email protected]:33307/adap
Example of returned result:
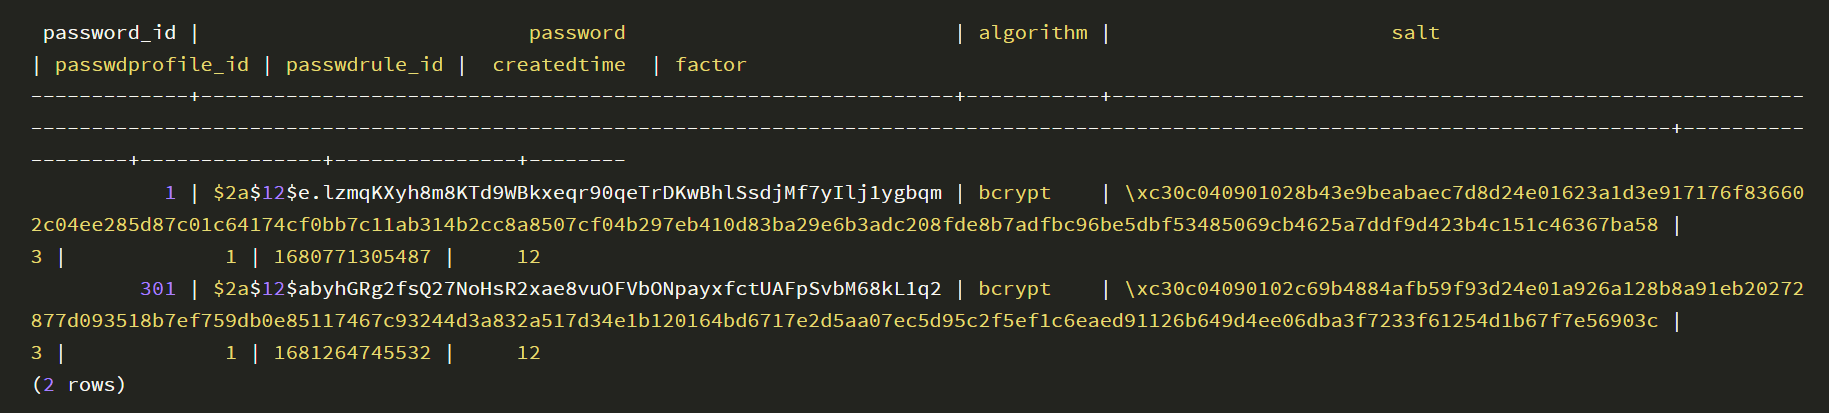
It is found that the data content of password is encrypted
0x05 Summary
After setting up the ADAudit Plus vulnerability debugging environment, we can then start learning about the vulnerabilities.


